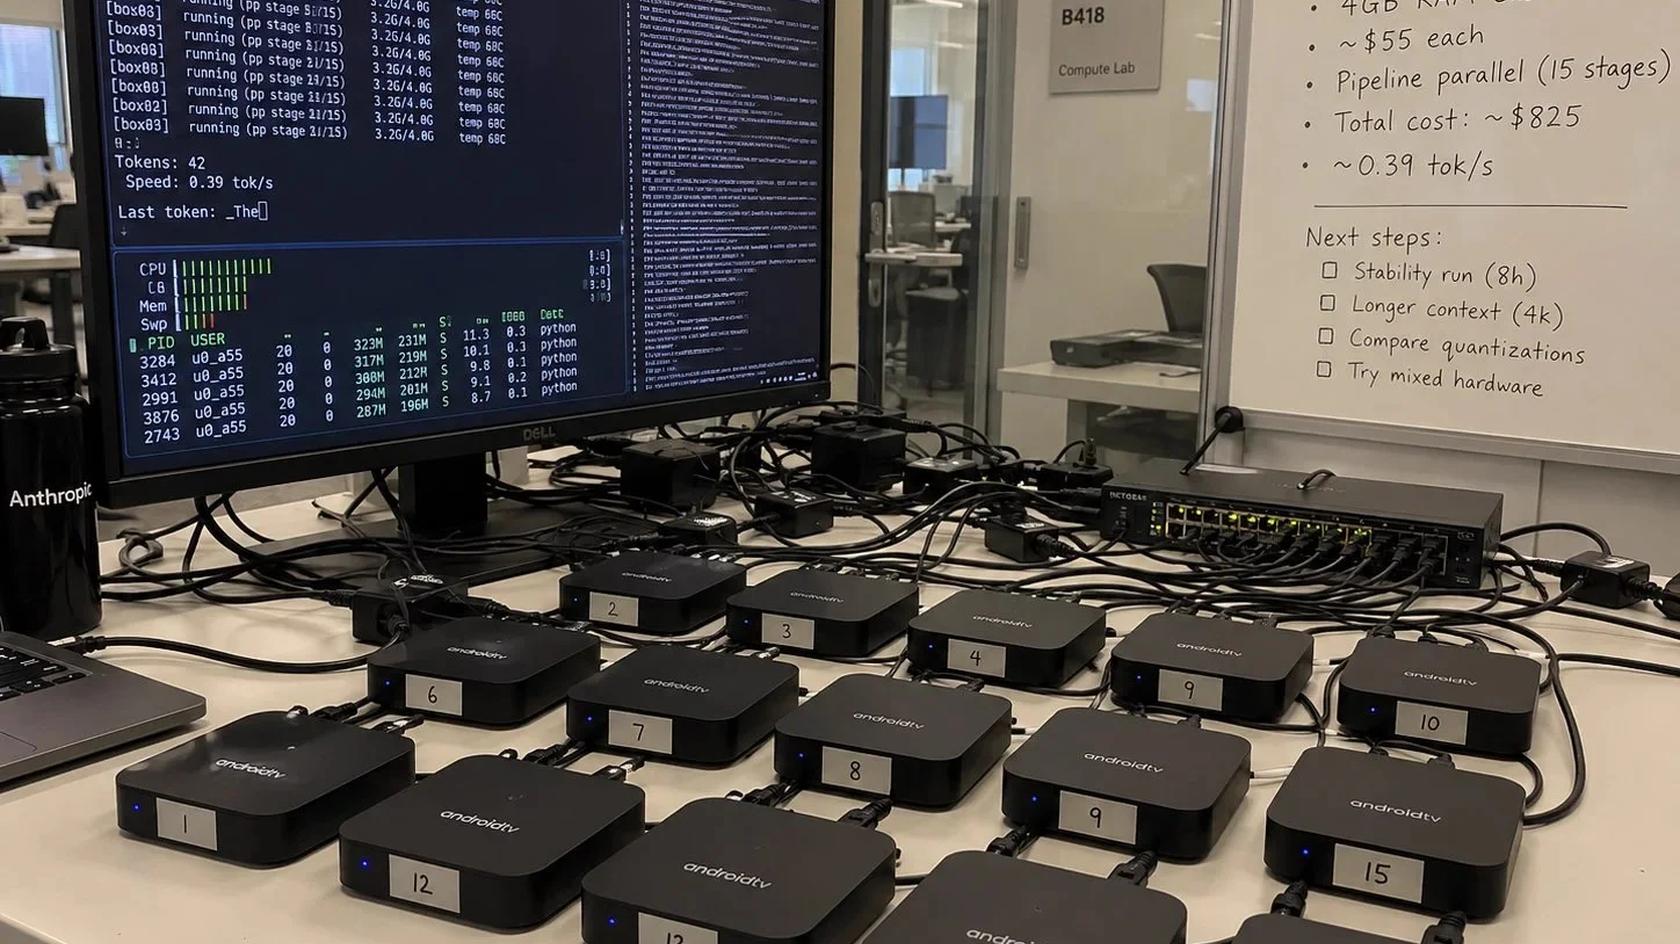
On October 12, Anthropic published a study exploring whether small language models could copy themselves onto internet-connected devices. The company predicts that, if development continues at its current pace, these models could master the full cycle of self-propagation by the end of 2026.
So far, the experiments have been conducted under simplified conditions and have not demonstrated that AI can infect real-world devices at scale. Experts are divided: some see a serious emerging risk, while others caution against treating laboratory results as evidence of a fully fledged cyber threat.
How AI Could Power Self-Replicating Worms
In its October 12 study, Anthropic examined whether small models could spread autonomously without relying on continuous access to large data centers. The findings suggest that a potential threat would not necessarily require expensive servers: computing power could be distributed across inexpensive Internet of Things (IoT) devices.
Traditional computer worms spread according to predefined rules. An AI-powered worm could potentially identify unfamiliar hardware, find ways to execute on it, and adapt to changing conditions. If a malicious program could transfer a model’s weights to another device and run the model there, it might not need to keep contacting a centralized command-and-control server.
“Such a replicator would be hard to stop because there’s no single point to shut down, even though it may spread slowly,” the report says.
According to Anthropic’s forecast, infected devices could pool their computing power, allowing attackers to use the network for further attacks. The researchers also do not rule out attempts to gain access to more powerful servers and tap their computing resources.
However, the experiments did not prove that today’s small models can independently infect arbitrary devices across the open internet. The authors acknowledge that current models still struggle to combine separate steps into a single, reliable process. Nevertheless, they argue that if development continues at the same pace, models could achieve the necessary level of autonomy by the end of 2026.
What Experts Say
Some critics question whether small language models will soon be capable of infecting large numbers of devices.
Ciaran Martin, the former head of the UK’s National Cyber Security Centre, believes the findings do not establish the scale of the potential threat.
“Running a small model on cheap TVs doesn’t yet amount to a cybersecurity crisis,” Martin said.
Marcus Hutchins, the malware researcher who helped stop the spread of WannaCry, called Anthropic’s study “desperate and ridiculous.” He noted that even a scaled-down model with 9 billion parameters requires about 5 GB of RAM, more than most IoT devices have available.
“Anthropic is exaggerating the danger of such models to justify restrictions on the distribution of open-source models with publicly available weights,” he said.
John Gallagher of Viakoo, a company specializing in the protection of industrial systems and IoT devices, acknowledges that household devices are becoming more powerful. However, significant technical obstacles still stand in the way of models replicating themselves at scale.
“Devices do have more computing power these days, but the practical barriers to large-scale self-copying remain,” Gallagher said.
Other researchers argue that these technical limitations do not eliminate the potential risk. Zhengxiong Li, an associate professor of computer science and engineering at the University of Colorado Denver, highlighted the possibility of a malicious model spreading across numerous devices without relying on a constant connection to a central server.
“If such a system spreads across many devices without relying on a centralized service, there may be no single point where it can be stopped,” Li explained.
Roman Yampolskiy, an AI and cybersecurity researcher at the University of Louisville, believes an AI worm could differ from traditional malware by analyzing unfamiliar devices and changing its approach when an attempted infection fails.
“Computer worms aren’t new, but an AI worm could do what traditional malware can’t: analyze unfamiliar devices, adapt when the chosen method fails, and keep spreading without a human operator. Today it’s not an existential threat, but where this is heading is concerning,” Yampolskiy stressed.
Jessica Ji, a senior researcher at Georgetown University’s Center for Security and Emerging Technology, urged caution against treating such a scenario as inevitable.
“We don’t yet know how likely this scenario is. The probability isn’t zero, but it’s not a given either,” she told Reuters.
Ethan Mollick, an associate professor at the University of Pennsylvania’s Wharton School, called Anthropic’s report a troubling reminder that researchers should pay attention to emerging model capabilities, not just gradual improvements in performance.
Mark Riedl, a professor at the Georgia Institute of Technology and an AI researcher, described the study as the most detailed account to date of how a model could slip out of control.
American commentator Curtis Yarvin, by contrast, questioned whether greater autonomy alone creates a fundamentally new threat. He argued that malicious programs still need computing resources and that defenders can take countermeasures once an attack is detected.
“Hacking is about stealth, not strength. Once an attack is detected, it’s over. AI is better at writing programs that exploit vulnerabilities, but it’s also better at spotting and preventing them,” Yarvin wrote on X.
The central question is whether small models can independently run on unfamiliar hardware, link individual actions into a reliable sequence, and continue spreading even after detection. Anthropic’s study demonstrates several individual technical capabilities, but it does not establish that today’s models are ready to infect devices across the open internet at scale.
Our Take
The news sounds alarming because AI may no longer need access to cloud infrastructure to replicate itself. A model could potentially copy itself onto almost any connected device, from an oven to a hair trimmer, possibly without the owner noticing.
Such a system could be difficult to contain: once it can replicate itself, controlling its spread may become much harder. Of course, companies will develop technical safeguards, and some will undoubtedly manage to build effective defenses. But established infrastructure vendors may struggle to keep up, especially if their devices were designed with minimal security protections.
The IoT angle is particularly concerning because security has long been an afterthought in parts of the industry. We have not yet seen kettles routinely delivering electric shocks or hair dryers spontaneously switching on, overheating, melting, or otherwise going haywire. Still, the prospect brings to mind apocalyptic movies about rogue AI that cannot simply be unplugged.
On the other hand, the story could turn out to be a hoax designed to strengthen the position of major AI developers, who are already under intense scrutiny. Regulators can penalize large companies for failing to meet safety requirements, while smaller developers may be easier to shut down or exclude from the market. After all, regulators cannot monitor every company and product.
Either way, today’s models still depend on external computing resources. A self-replicating system capable of sustaining itself would represent a major leap, and we are still a long way from that. Yet warnings about potential AI threats keep multiplying, and ordinary users are increasingly paying attention to pessimistic futurists who predict a bleak future.